
The situation
The business wants agents and RAG over documents and datasets spread across stores. Security will not hand an agent raw cloud keys, and nobody wants to copy everything into one place first.What OneBucket changes
The data plane speaks MCP natively, with OAuth 2.1 and audience-bound tokens. A policy sets the outer limits per key; inside them the agent lists, reads and writes at runtime. Every call is logged, and a key can be dropped to read-only instantly.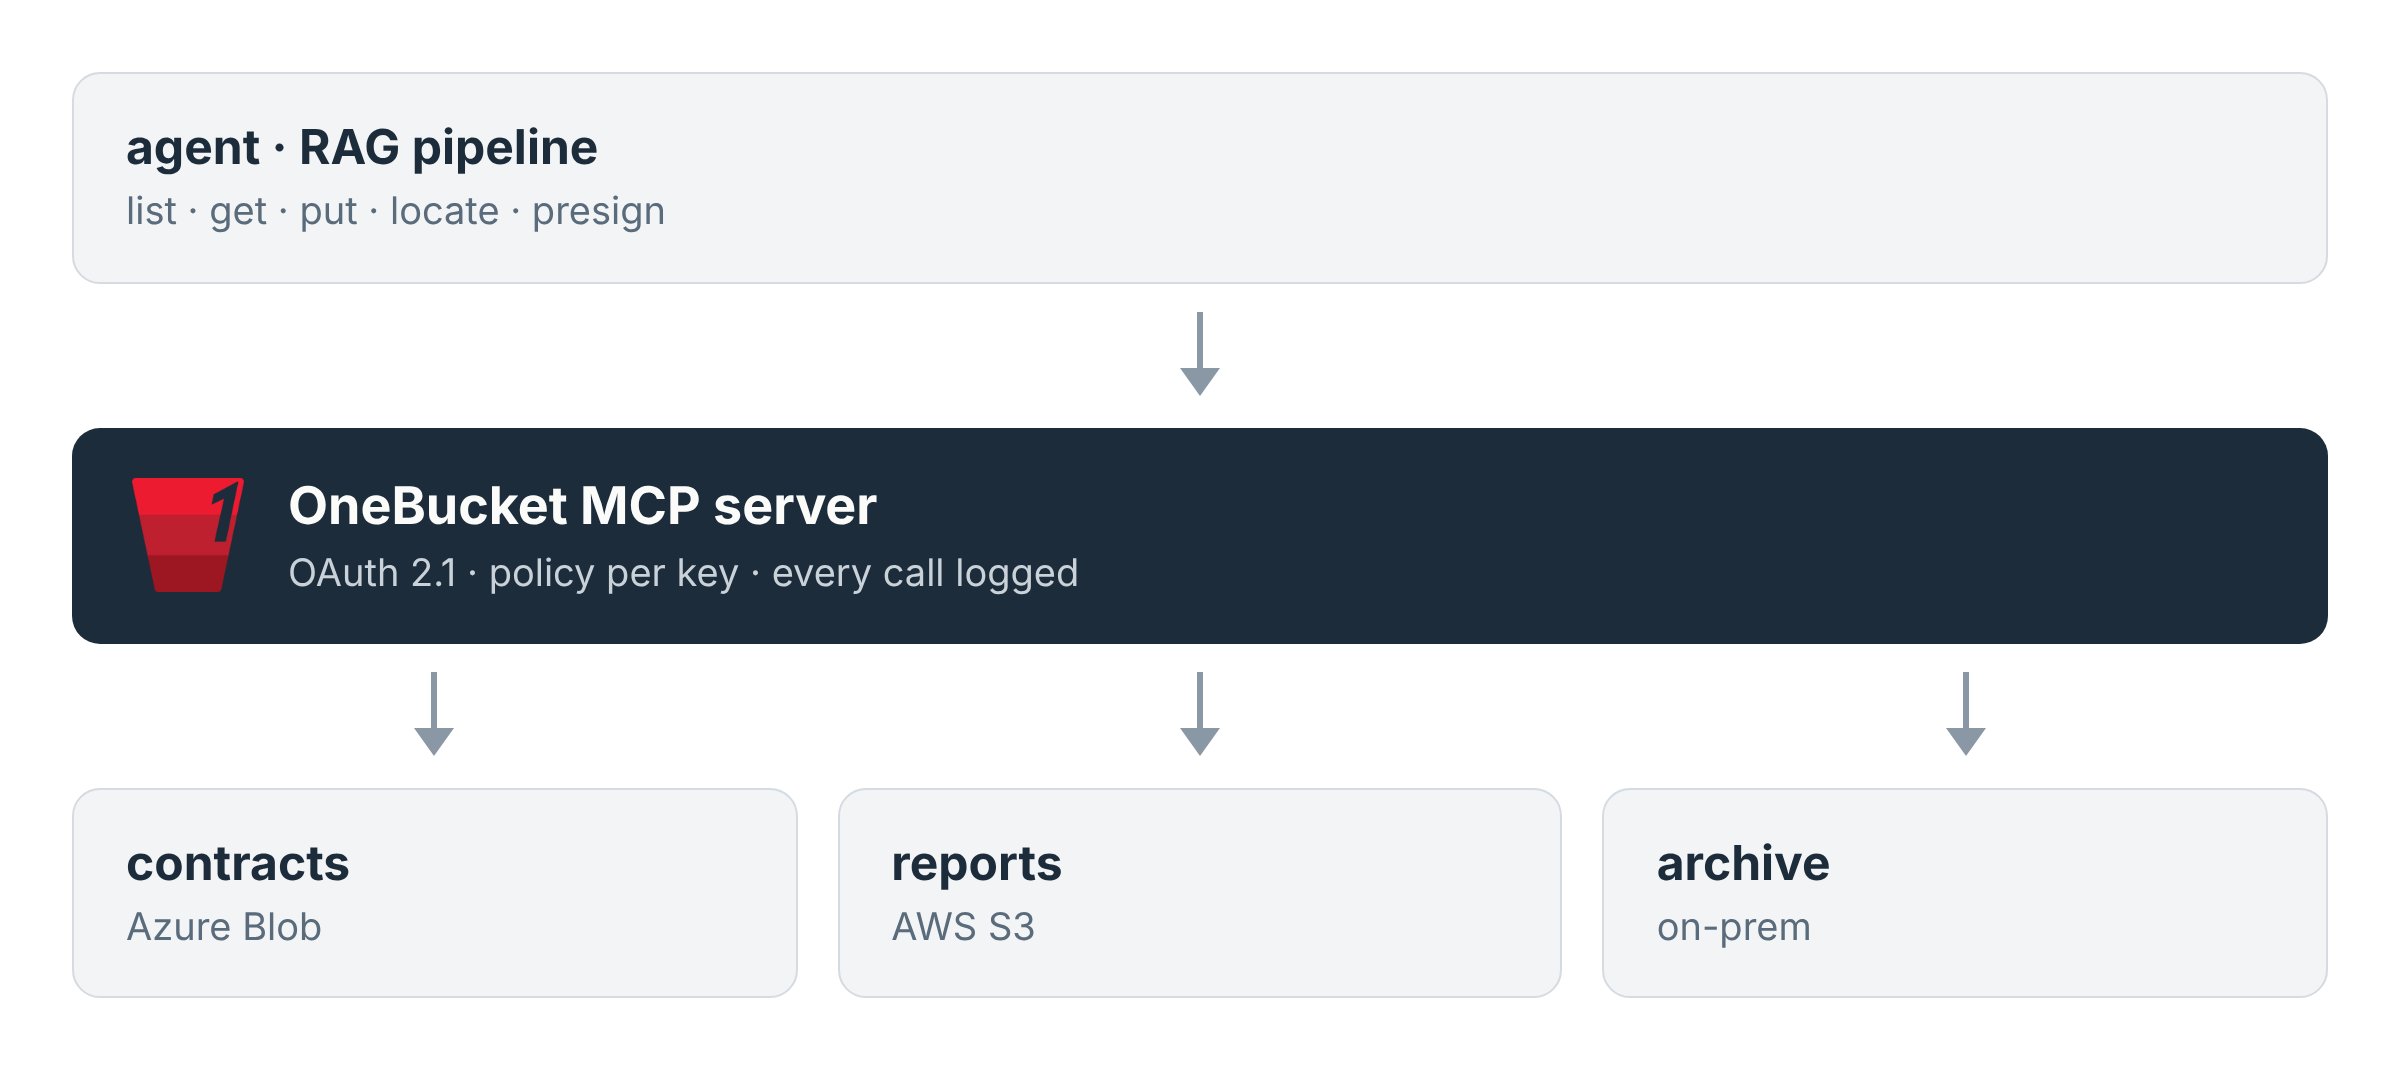
How it works
- No cloud keys on the agent. The agent authenticates to OneBucket with OAuth 2.1 (PKCE), gets a token bound to one audience, and operates under the policy attached to its key. Backend credentials never leave the secure vault.
- Tools.
list,head,get,put,copy,move,migrate,locate,prefetchandpresignover the Core MCP. Large objects are handed back as presigned URLs so they bypass the model. - Kill switch. Reassign a key from a read/write policy to a read-only policy and the next write fails, with the attempt visible on the event stream.
- Audit. Every operation is an event, scoped to organization and key, listed and tailed over the Events MCP.
- Nothing to install. OneBucket ships as an MCP connector in Claude and works with any MCP client.
Related
- Claude connector
- How authentication works: OAuth 2.1, audience binding
- Fewer tokens: know before fetching